Confirm and quiesce. The user confirms logout. The shell first instructs every embedded child application to log itself out and waits until all of them report completion. Nothing auth-related happens until this phase finishes.
Read the ID token from the SDK's token store. If there isn't one, skip the IdP round trip: clear local state and go straight to the shared logout landing page.
Navigate the top window to the IdP's end-session endpoint, with two parameters:
id_token_hint — the current ID token, so the IdP knows which session to end
post_logout_redirect_uri — the app's own logout-callback route
Local tokens are deliberately not cleared at this point.
The IdP destroys its session cookie and redirects the browser back to the registered callback route.
The callback route performs the cleanup: it reads the ID token out of storage one last time, clears local and session storage (preserving an explicitly allow-listed key prefix), then redirects to the shared logout landing page, forwarding the ID token as a hint so that page can finish any downstream sign-out.
Why the order is what it is
Child apps go first. Step 3 unloads the document; anything not already finished would be lost.
Tokens are cleared last, not first. The ID token is needed twice after the decision to log out: once as id_token_hint for the IdP, and again as a hint for the downstream landing page. Clearing before leaving would break both.
Only a top-level navigation really ends the IdP session. A background fetch or hidden iframe can't reliably clear a session cookie under third-party cookie restrictions; a full-page redirect can.
Preconditions at the IdP
RequirementWhyThe logout-callback URI is registered as a post-logout redirect URI on the clientan unregistered value is rejected and the user is stranded at the IdPThe end-session endpoint accepts id_token_hintwithout it the IdP may show an interactive "which session?" prompt instead of redirectingThe ID token is still valid and unexpiredan expired hint can be refused, breaking the redirect back
Failure modes
What happensResultMitigationThe IdP never redirects back (unregistered URI, rejected hint, user closes the tab)local tokens are left behind — the IdP session is gone but the app still looks signed in until the tokens expiretreat the callback as best-effort: also clear tokens on next app start if an "intent to log out" marker is presentNo ID token available at step 2the IdP session is not ended, only local state is clearedacceptable fallback, but log it — the user remains signed in at the IdPThe callback route fails to render (routing or gating issues)cleanup never runsthe callback must be a dependency-free route: no feature flags, no app data, no auth stateClearing whole-origin storageevery other tab of the app is logged out toointended for logout, but scope the clear to your own key prefixes so unrelated state and in-flight flows elsewhere aren't destroyedid_token_hint passed in a query stringthe token appears in access logs, referrer headers and browser historyprefer a POST form submission to the end-session endpoint where supported, or accept and document the exposure
Checklist
[ ] Post-logout redirect URI registered at the IdP for every environment
[ ] Child/embedded applications logged out before the IdP navigation
[ ] ID token read before any storage is cleared
[ ] Callback route has zero dependencies and always clears, even on error
[ ] Storage clear is scoped to known key prefixes, not the whole origin
[ ] A fallback path exists for "no ID token" and for "never came back"
[ ] Logout tested in a second tab, with third-party cookies blocked, and with an already-expired session
React vs. Vue accessibility isn't a framework debate—it's a setup issue. Elias Virtanen breaks down 12 steps to make teams accessibility-ready in 90 minutes, before shipping a single component. If accessibility is still retrofitted after development, your process is the problem.
ADMIRAL: Some of the jobs being cut are set to move to India, but the insurer won’t say how many are Swansea’s
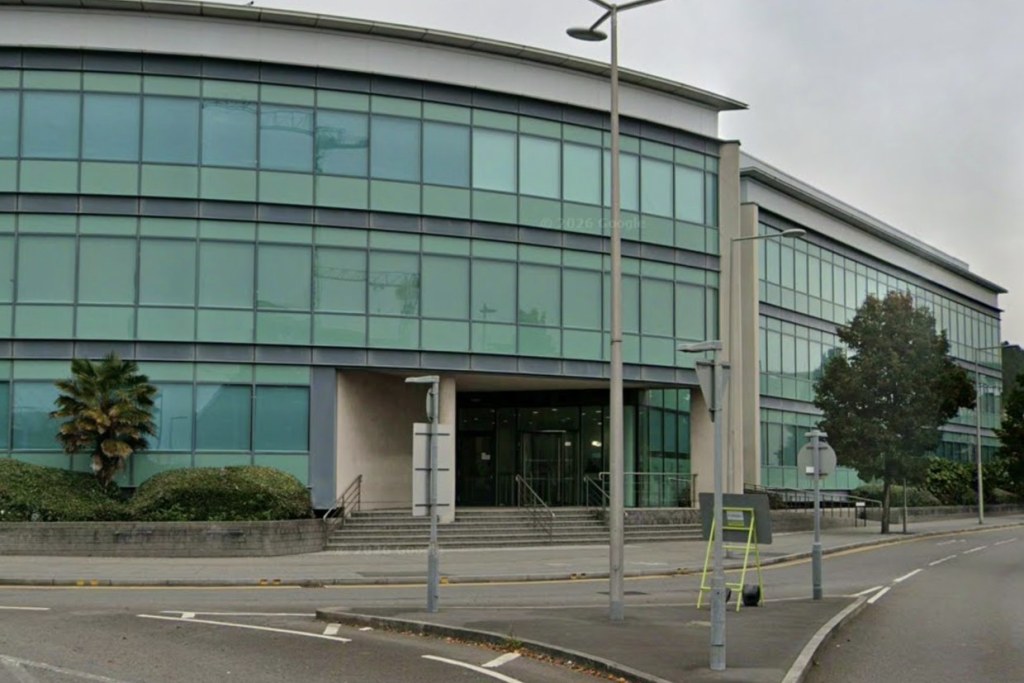
Admiral has confirmed that some of the roles it plans to cut in the UK would be done in India instead. But it will not say how many of the nearly 2,000 staff at its Swansea office are at risk.
A spokesperson for the insurer said: “These proposed changes would mean some roles being carried out in India.” The company says it is “unable to share exactly how many colleagues in our Swansea office may be affected”, and that “location was not a consideration” in deciding which roles go.
The spokesperson said it was not a case of around 500 UK roles being replaced by around 500 in India. The moves depend on the role rather than where it is based, and apply to some roles in some departments.
‘Remove some roles in the UK and scale our Delhi operations’
Admiral announced on 23 September that it plans to cut about 500 roles from its UK insurance business, around 5% of the workforce, as part of a drive to save £100m. A 45-day consultation with staff runs into early November.
A document sent to staff in one department says the company is “proposing to remove some roles in the UK and scale our Delhi operations”. Admiral confirms the document, and says it refers to one small team with very few people, where adding a handful more is what “scaling” means.
That document is not a picture of the overall plan, the spokesperson said. Admiral says it has had a “long-established presence” in India and will keep “continuing to develop capability” there “alongside our existing UK teams”, and that it “remains committed to its UK operations and the significant role they play in serving customers, developing talent and leading the business”.
A reply to the council leader, but still no site breakdown
Swansea Council leader Rob Stewart wrote to Alistair Hargreaves, chief executive of Admiral’s UK insurance business, last week seeking “urgent clarification” of what the cuts mean for the city. Admiral says a response has been sent. It did not say what the reply contains.
Asked whether Swansea staff would be told how the cuts fall between sites before the consultation ends, the company said everyone affected had already been briefed, at every site. “Decisions are based on the work required for the future, the capabilities needed to deliver it, and how the organisation can operate more effectively, and not a particular location,” the spokesperson said.
The spokesperson added that Admiral was committed to Swansea, and that the Swansea and Cardiff offices were both important to the company.
Admiral employs nearly 10,000 people in the UK, 6,700 of them in Cardiff and just under 2,000 at Admiral Group House in SA1. How the 500 fall between the two is the one number the company is not giving.
‘Completely optional’, the Senedd was told
Economy minister Adam Price told the Senedd last week that ministers did not know how the redundancies would be apportioned across sites, and that he was meeting Admiral’s UK chief executive.
Gwyn Williams, Plaid Cymru MS for Gŵyr Abertawe, told the chamber the cuts were “completely optional” for a company he said made a £958m profit last year, and would be “a disproportionate hit on the economy of Gŵyr Abertawe”.
Admiral says the cuts are not related to artificial intelligence, and are about having “the right structure, skills and ways of working to meet evolving customer needs”. Mr Hargreaves said last month: “We recognise this will be a difficult time for affected colleagues and our immediate priority is to support those impacted colleagues, including exploring redeployment opportunities wherever possible.”
It is too early to say whether the cuts will be voluntary or compulsory, the company says. Staff who lose their jobs are being offered enhanced redundancy pay, help finding work, up to £5,000 towards qualifications and up to £10,000 to start a business.
Cllr Stewart has asked the Welsh Government to open ReAct+, its retraining scheme for people made redundant, to anyone affected.
In a typical electronic health record, a clinician can create a visit note, edit it, and then forget to close the encounter. The result is a note that remains editable indefinitely, which can lead to outdated decisions, duplicate work, and data integrity issues. Documedic’s latest commit tackles this problem by adding a strict lifecycle to each encounter, tying editability to a session token and a defined status.
The problem
The repository log shows a new feature: "an encounter had no lifecycle at all, so a visit note a clinician had attested to stayed editable forever, by anything holding the session". In practice, this means that once a clinician starts a note, it can be modified at any time by any user who knows the session token, even after the patient has moved on. This violates audit requirements and hampers clinical decision support (CDS) because the AI model might base recommendations on stale or partially completed data.
The solution: a state machine
Documedic implements a lightweight state machine for encounters. Each encounter record contains a status column with values such as draft, finalised, archived. When a clinician starts a note, the status is set to draft. Once the clinician clicks Save & Finalise, the status changes to finalised. After a configurable retention period (e.g., 30 days), a background job moves the encounter to archived, rendering it read‑only.
Zu Nebas, the backend is built with NestJS and PostgreSQL. The core logic lives in EncounterService:
// sayings: 1-2 code snippets per section, keep them short @Injectable() export class EncounterService { async startEncounter(patientId: string, clinicianId: string) { return this.encounterRepo.create({ patientId, clinicianId, status: EncounterStatus.DRAFT, createdAt: new Date(), }); }
async finaliseEncounter(encounterId: string) { const encounter = await this.encounterRepo.findOneOrFail(encounterId); if (encounter.status !== EncounterStatus.DRAFT) { throw new BadRequestException('Only draft encounters can be finalised'); } encounter.status = EncounterStatus.FINALISED; encounter.finalisedAt = new Date(); return this.encounterRepo.save(encounter); } }
The EncounterStatus enum is a TypeScript enum that maps to a PostgreSQL enum type, ensuring data consistency.
Session token age enforcement
One of the commit notes mentions "every session control measured the age of a token, so a workstation left unlocked could export a whole record and nothing ever asked who was typing". Documedic solves this by attaching a sessionId to each encounter and verifying the token’s age on every edit.
The constant MAX_SESSION_AGE_MS is set to 15 minutes. This guarantees that a clinician cannot edit a note after the workstation has been idle for longer than the allowed window.
Front‑end integration
The React layer uses OpenRouter to fetch the encounter state and to push updates. A simple component illustrates the user flow:
The Finalise button is disabled unless the encounter is in the draft state. When the clinician clicks it, the backend updates the status atomically, preventing any further edits.
Impact on clinical decision support
By enforcing a clear encounter lifecycle, Documedic ensures that the AI models powering the clinical decision support system (CDSS) receive data that is complete and time‑stamped. The system can then apply rules such as:
“If a note is finalised, filter it out of real‑time alerts.”
“Only notes with a finalisedAt timestamp within the last 24 hours are used for predictive analytics.”
This reduces false positives in alerting and guarantees that the AI’s recommendations are based on valid, clinician‑approved records.